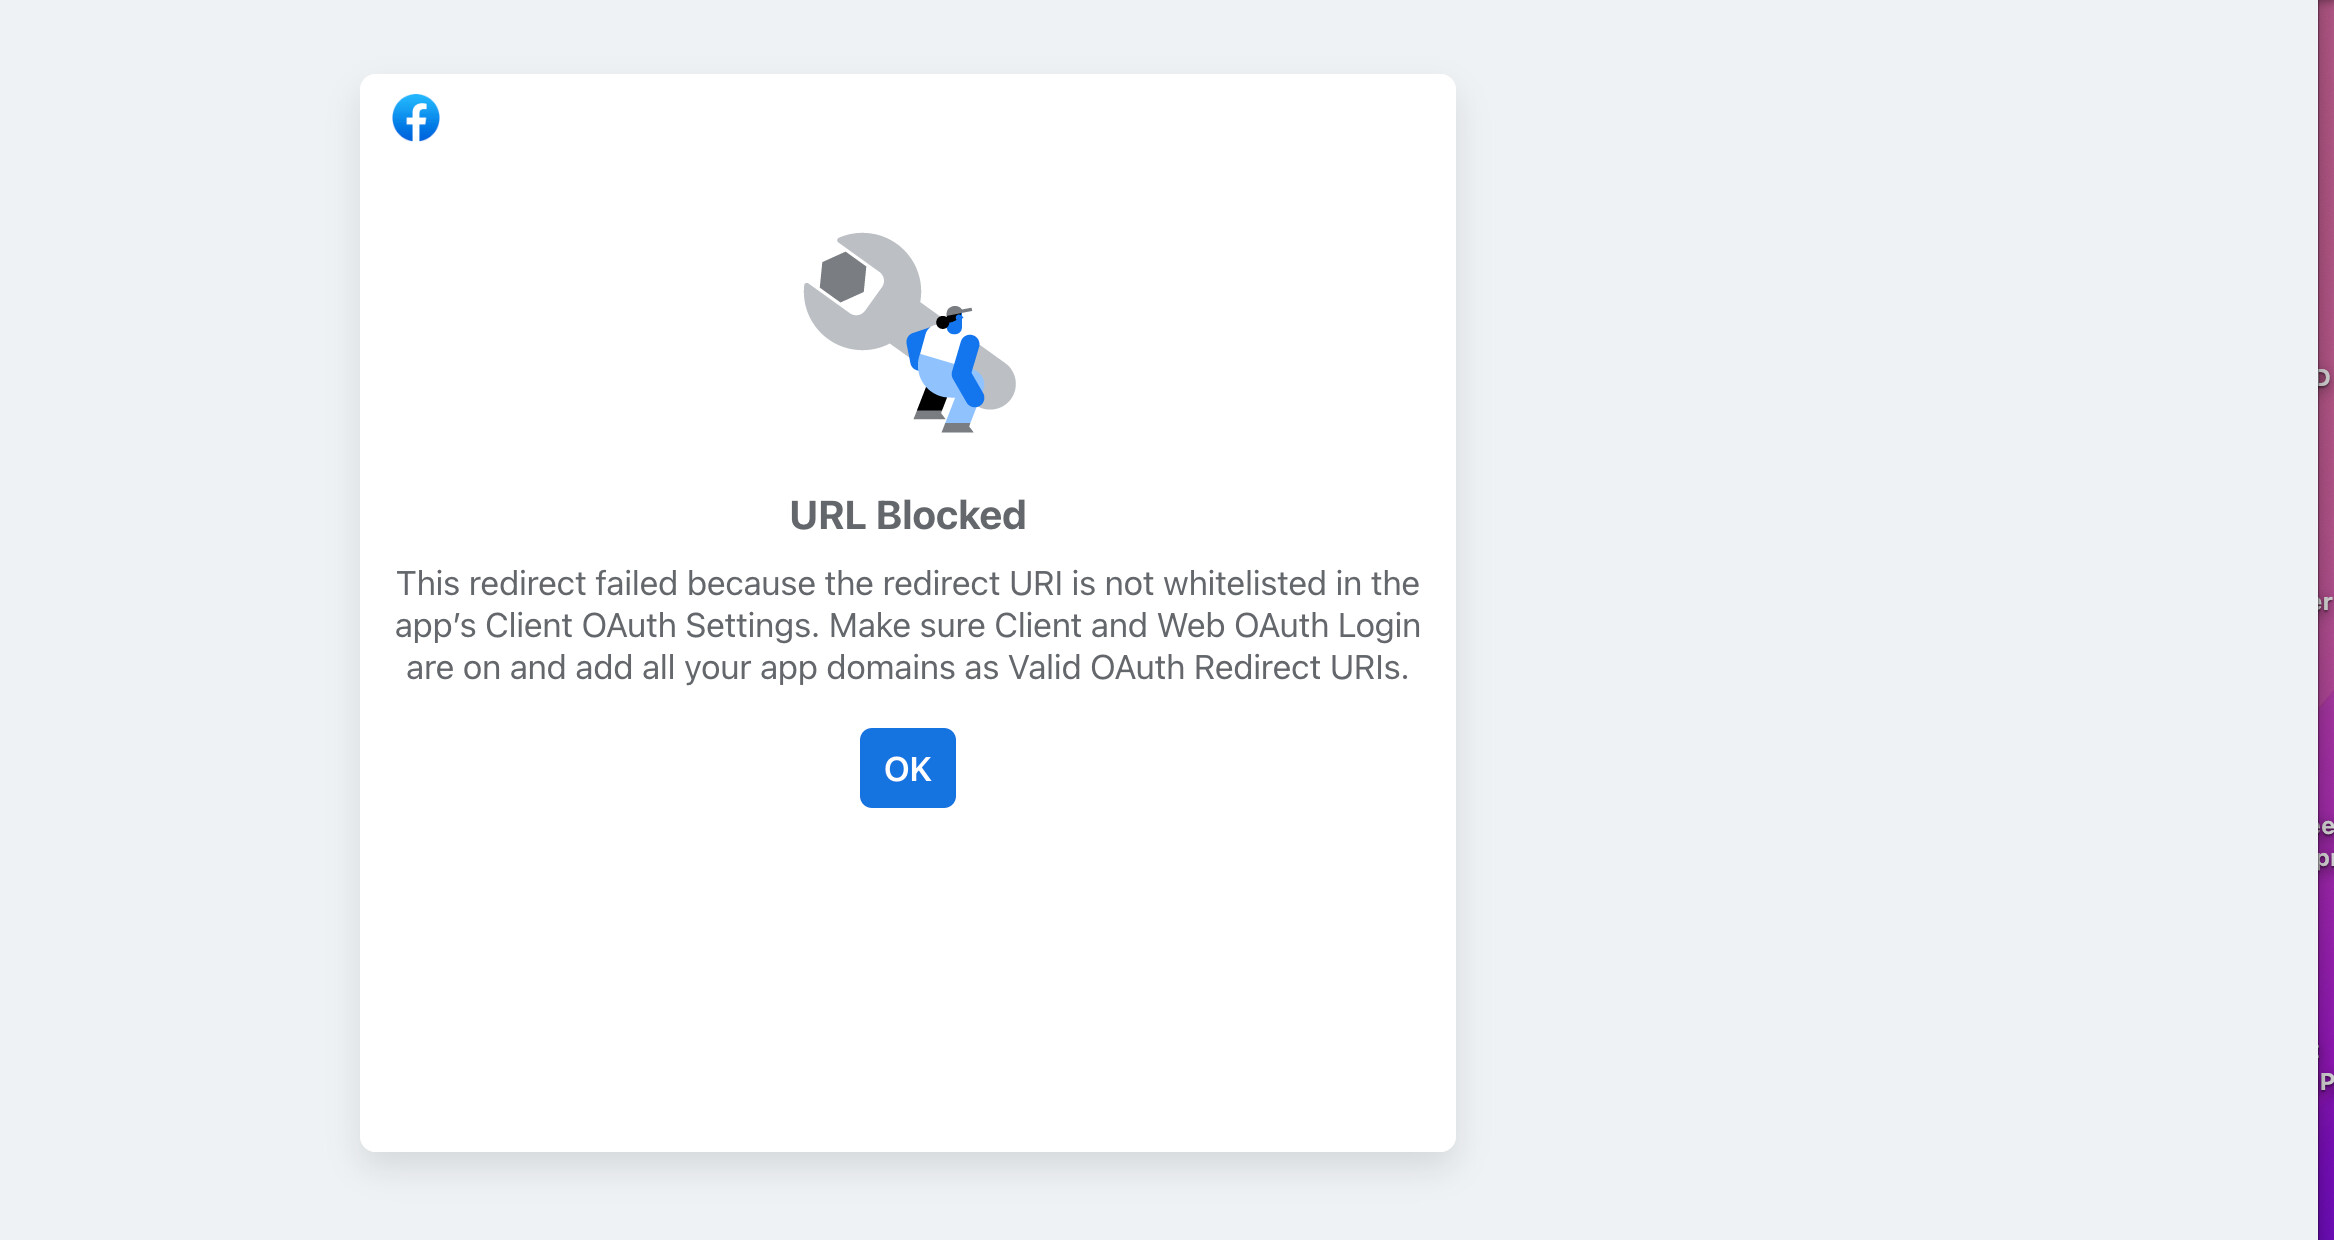
I am trying to use facebook login provider. There are two callback urls in the facebook login provider - one starting with https://api.backendless.com/ …/users/oauth/facebook/authorize
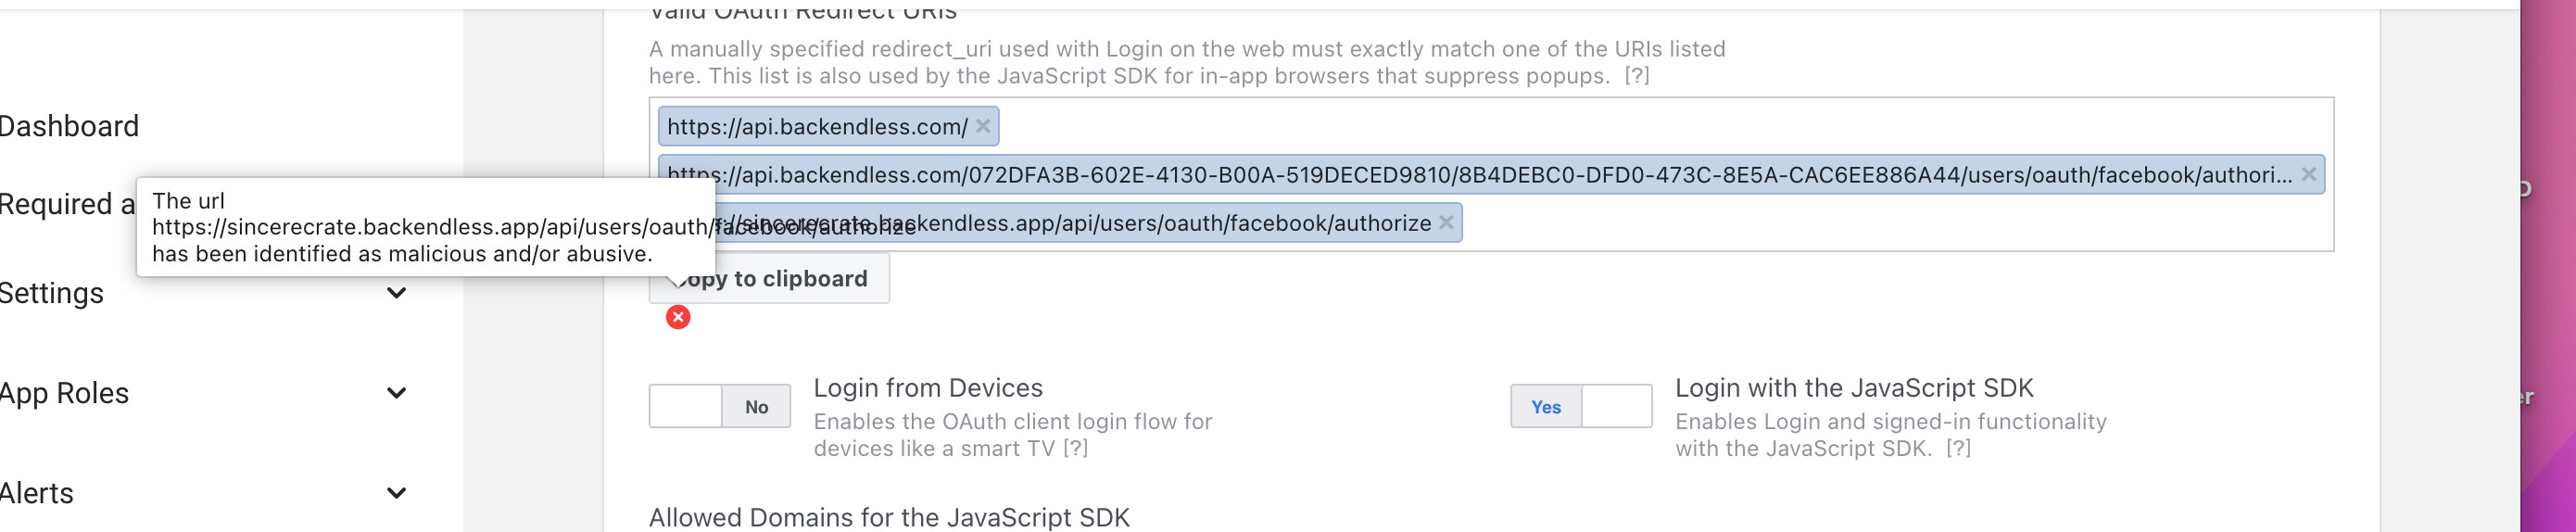
and other with https://sincerecrate.backendless.app/api/users/oauth/facebook/authorize. Now when I add sincerecrate url in facebook setup, I get message that * The url https://sincerecrate.backendless.app/api/users/oauth/facebook/authorize has been identified as malicious and/or abusive. Please see the screenshot.
Irrespective of whether I add that url or not, the code always redirects to https://sincerecrate.backendless.app/api/users/oauth/facebook/authorize&scope=email&state=2ac197a8-aa86-4d13-ab7e-f589635a678b. Then I get error “This redirect failed because the redirect URI is not whitelisted in the app’s Client OAuth Settings. Make sure Client and Web OAuth Login are on and add all your app domains as Valid OAuth Redirect URIs.” How do I get rid of the issue?